| EnrollmentPatterns |
An array of objects containing the enrollment patterns available for enrollment by the user.  Show enrollment pattern details.
| AllowedEnrollmentTypes |
An integer indicating the allowed enrollment types for the enrollment pattern. This value controls which enrollment methods can be used through the Keyfactor API and Management Portal.
For CSR and PFX enrollment, the enrollment pattern is only available when associated with a CA that is configured for enrollment in Keyfactor Command (see HTTPS CAs - Enrollment Section or DCOM CAs - Enrollment Section).
Show allowed enrollment type details.
| 0 |
None |
| 1 |
PFX Enrollment |
| 2 |
CSR Enrollment |
| 3 |
CSR Enrollment & PFX Enrollment |
| 4 |
CSR Generation |
| 5 |
CSR Generation & PFX Enrollment |
| 6 |
CSR Generation & CSR Enrollment |
| 7 |
CSR Enrollment, PFX Enrollment & CSR Generation |
|
| CAs |
An array of objects indicating the certificate authorities configured for use with the enrollment pattern. If the RestrictCAs parameter is set to True, this will be limited to the CAs configured in the CertificateAuthorities parameter of the enrollment pattern. Show CA details.
| DisplayName |
A string indicating the certificate authority display name, which may be the same as the reference name. If the Enrollment > General > Display CA Hostname application setting is turned off, DCOM CAs will display only the logical name (for example, CorpIssuing1).
|
| Id |
An integer indicating the Keyfactor Command reference ID of the CA. |
| Name |
A string indicating the certificate authority reference name:
-
For DCOM configurations, the DNS host name and CA logical name in the format hostname\logical name (for example, ca1.keyexample.com\CorpIssuing1)
-
For HTTPS configurations, the CA URL (for example, https://ca1.keyexample.com)
|
| RFCEnforcement |
A Boolean that indicates whether RFC 2818 compliance enforcement is turned on (True or False). When this option is set to True, certificate enrollments made through Keyfactor Command for this CA must include at least one DNS SAN.
In the Keyfactor Command Management Portal, this causes the following behavior:
-
PFX Enrollment: The CN entered in PFX enrollment is automatically replicated as a DNS SAN, which the user does not see and cannot change.
-
CSR Enrollment: If the CSR does not have a SAN that matches the CN, one will automatically be added to the certificate. The user enrolling does not see this and cannot change it.
-
CSR Generation: The CN entered will be automatically replicated as a DNS SAN and set to read only.
Tip: The RFCEnforcement option at the CA level is used only for standalone CAs. RFC enforcement for enterprise CAs is configured on at the enrollment pattern level (see POST Enrollment Patterns).
|
| SubscriberTerms |
A Boolean that sets whether to add a checkbox on the enrollment pages to force users to agree to a custom set of terms before enrolling (True or False). The default is False.
Note: The subscriber terms setting does not apply to enrollments done through the Keyfactor API.
Tip: Configure a link to the custom terms using the Enrollment > General > URL to Subscriber Terms application setting. See Application Settings: Enrollment Tab for more information.
|
|
| ConfigurationTenant |
A string indicating the configuration tenant of the template. For Microsoft templates, this field is populated from Active Directory. For EJBCA templates, this field is populated from the Keyfactor Command CA record. The field is not configurable.
|
| EnrollmentFields |
An array of objects defining custom enrollment fields for an enrollment pattern. These fields allow additional request attributes to be included with CSR and PFX enrollments and passed to the certificate authority (CA) during the enrollment process.
Custom enrollment fields can be used to:
-
Enforce certificate request requirements and prevent invalid enrollments
-
Provide additional information to the CA as part of the request
-
Support integrations such as the Keyfactor Windows Enrollment Gateway, which uses enrollment fields for standard functionality
When configured, these fields are presented during CSR and PFX enrollment (for example, in the Additional Enrollment Fields section in the Management Portal) and must be completed as part of the request. The submitted values are passed to the CA and may appear in CA-issued certificate attributes, depending on CA configuration.
Note: These fields are not metadata and are not stored in Keyfactor Command. They are passed through to the CA, where they can be used by a gateway or policy module to perform additional processing.
Show enrollment field details.
| DataType |
An integer indicating the parameter type. The options are:
| 1 |
String: A free-form data entry field. |
| 2 |
Multiple Choice: Provides a list of acceptable values for the field. The multiple choice values are provided in the Options parameter. |
|
| Id |
An integer indicating the ID of the custom enrollment field. |
| Name |
A string indicating the name of the custom enrollment field. This name will appear on the enrollment pages. |
| Options |
For multiple choice values, an array of strings containing the value choices. |
|
| ExtendedKeyUsages |
Currently not in use. |
| Id |
An integer indicating the ID of the enrollment pattern in Keyfactor Command. |
| IsDefaultTemplate |
A Boolean indicating whether this enrollment pattern is the default pattern for the associated template (True or False). A certificate template can have only one default enrollment pattern, which is required for the template to be used for enrollment. If no other enrollment pattern for the template exists or is marked as default, this option will automatically be enabled when a new pattern is created.
|
| Name |
A string indicating the Keyfactor Command reference name of the enrollment pattern. |
| RequiresApproval |
A Boolean indicating whether the template has been configured with the Microsoft CA certificate manager approval option active (True or False).
Important: Any templates that are configured on the Microsoft CA Issuance Requirements tab for CA certificate manager approval cannot be used for enrollment and associated alerting in Keyfactor Command without configuring private key retention. Any of the active private key retention settings (settings other than none as described for KeyRetention) will allow a template requiring manager approval to work with Keyfactor Command PFX and CSR enrollment. 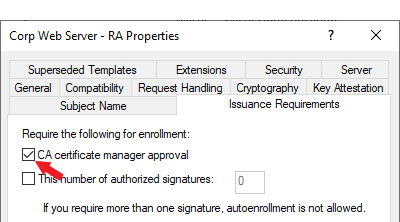
Figure 638: Microsoft Issuance Requirements on a Template for Manager Approval
|
| ResolvedDefaults |
An array of objects representing the default certificate subject values displayed during enrollment in the Management Portal. These values are used to prepopulate subject fields in the Management Portal. Each subject part appears once, using the enrollment pattern default if defined. Otherwise, the system-wide default is used.
Note: Enrollment defaults do not apply to requests made with CSR enrollment or the Keyfactor API.
|
| ResolvedMetadataFields |
An array of objects representing the certificate metadata fields and their default values that will be applied during enrollment. Each field appears once and reflects the effective default value for the enrollment pattern. If a default is defined at the enrollment pattern level, it is used. Otherwise, the system-wide default is applied. |
| ResolvedPolicies |
An object representing the policies applied during certificate enrollment. This object defines constraints and behavior such as allowed key algorithms, key reuse, wildcard support, and certificate ownership. The values reflect the effective policy for the enrollment pattern, with enrollment pattern settings taking precedence over system-wide defaults. |
| ResolvedRegexes |
An array of objects representing the regular expressions used to validate certificate subject data during enrollment. Each field appears once and includes the effective validation rule. If a validation rule is defined at the enrollment pattern level, it is used. Otherwise, the system-wide rule is applied. |
| TemplateCommonName |
A string representing the short name (common name) of the certificate template. For a template created using a Microsoft management tool, this will be the Microsoft template name, which typically does not contain spaces. For templates associated with an EJBCA CA, the name is usually constructed using the format end entity profile name_certificate profile name. If the end entity profile and certificate profile share the same name, only the end entity profile name is used. This field is populated based on information retrieved from the CA and is not configurable.
|
| TemplateName |
A string containing the name of the template. For a template created using a Microsoft management tool, this will be the Microsoft template display name. For a template generated for an EJBCA CA, this will be built using a naming scheme of end entity profile name (certificate profile name). This field is populated based on information retrieved from the CA and is not configurable.
|
|
| Standalone CAs |
An array of objects containing enrollment information for standalone certificate authorities available for enrollment for the current user. Show standalone CA details.
| Name |
The full name of the CA, made up of the DNS host name of the certificate authority (for example, myca.keyexample.com) and the logical name (for example, CorpStandaloneCA1) for a full name similar to myca.keyexample.com\\CorpStandaloneCA1. |
| RFC Enforcement |
A Boolean that sets whether certificate enrollments made through Keyfactor Command for this CA must include at least one DNS SAN (True or False). In the Keyfactor Command Management Portal, this causes the CN entered in PFX enrollment to automatically be replicated as a SAN, which the user can either change or accept. For CSR enrollment, if the CSR does not have a SAN that matches the CN, one will automatically be added to the certificate if this is set. This setting at the CA level applies only to standalone CAs. For CAs that use templates, this setting is controlled at the template level and is ignored at the CA level. |
| Subscriber Terms |
A Boolean that sets whether to add a checkbox on the enrollment pages to force users to agree to a custom set of terms before enrolling (True or False).Tip: Configure a link to the custom terms using the Enrollment > General > URL to Subscriber Terms application setting. See Application Settings: Enrollment Tab for more information. |
|
| Templates |
An array of objects containing the templates available for enrollment by the user. Show template details.
| CAs |
An array of objects indicating the certificate authorities that allow enrollment for the template and the requesting user. The template must be available for enrollment on the CA, the template and CA must be configured for enrollment in Keyfactor Command, and the requesting user must have enrollment permissions. Show CA details.
| Name |
A string indicating the full name of the CA, made up of the DNS hostname of the certificate authority (for example, corpca01.keyexample.com) and the logical name (for example, CorpIssuingCA1) for a full name similar to corpca01.keyexample.com\\CorpIssuingCA1. |
| RFC Enforcement |
A Boolean that sets whether certificate enrollments made through Keyfactor Command for this CA must include at least one DNS SAN (True or False). In the Keyfactor Command Management Portal, this causes the CN entered in PFX enrollment to automatically be replicated as a SAN, which the user can either change or accept. For CSR enrollment, if the CSR does not have a SAN that matches the CN, one will automatically be added to the certificate if this is set. This setting at the CA level applies only to standalone CAs. For CAs that use templates, this setting is controlled at the template level and is ignored at the CA level. |
| Subscriber Terms |
A Boolean that sets whether to add a checkbox on the enrollment pages to force users to agree to a custom set of terms before enrolling (True or False).Tip: Configure a link to the custom terms using the Enrollment > General > URL to Subscriber Terms application setting. See Application Settings: Enrollment Tab for more information. |
|
| Curve |
A string indicating the OID of the elliptical curve algorithm configured for the template, for ECC templates.
Note: This parameter is considered deprecated and may be removed in a future release.
|
| Display Name |
A string containing the common name (short name) of the template. This name typically does not contain spaces. For a template created using a Microsoft management tool, this will be the Microsoft template name. |
| Enrollment Fields |
An array of objects defining custom enrollment fields for a template. These fields allow additional request attributes to be included with CSR and PFX enrollments and passed to the certificate authority (CA) during the enrollment process.
Custom enrollment fields can be used to:
-
Enforce certificate request requirements and prevent invalid enrollments
-
Provide additional information to the CA as part of the request
-
Support integrations such as the Keyfactor Windows Enrollment Gateway, which uses enrollment fields for standard functionality
When configured, these fields are presented during CSR and PFX enrollment (for example, in the Additional Enrollment Fields section in the Management Portal) and must be completed as part of the request. The submitted values are passed to the CA and may appear in CA-issued certificate attributes, depending on CA configuration.
Note: These fields are not metadata and are not stored in Keyfactor Command. They are passed through to the CA, where they can be used by a gateway or policy module to perform additional processing.
Show enrollment field details.
| DataType |
An integer indicating the parameter type. The options are:
| 1 |
String: A free-form data entry field. |
| 2 |
Multiple Choice: Provides a list of acceptable values for the field. The multiple choice values are provided in the Options parameter. |
|
| Id |
An integer indicating the ID of the custom enrollment field. |
| Name |
A string indicating the name of the custom enrollment field. This name will appear on the enrollment pages. |
| Options |
For multiple choice values, an array of strings containing the value choices. |
For example:
Copy
"EnrollmentFields": [
   {
      "Id": 3,
      "Name": "MyCustomField",
      "Options": ["Green","Red","Yellow","Blue"],
      "DataType": 2
   }
]
|
| Enrollment Template Policy |
An object containing the individual template-level template policy settings. Template policies defined on a template apply to enrollments made with that template only. Template-level policies, if defined, take precedence over system-wide template policies. For more information about system-wide template policies, see GET Templates Settings. Show template policy details.
| Allow Key Reuse |
A Boolean that indicates whether private key reuse is allowed (True or False). This option applies to certificate renewals. By default, this is set to true at a system-wide level. |
| Allow Wildcards |
A Boolean that indicates whether wildcards are allowed (True or False). By default, this is set to True at a system-wide level. |
| AlternativeKeyAlgorithms |
An array of objects containing the supported alternative key algorithms for the template including the bit lengths and/or curves as appropriate. Show alternative key algorithm details.| name | A string indicating the name of the key algorithm. The supported key algorithm names are: ECDSA RSA Ed448 Ed25519 ML-DSA-44 ML-DSA-65 ML-DSA-87
| | bit_lengths | An array of integers indicating the key sizes supported for enrollment through Keyfactor Command. For RSA, Keyfactor Command supports key sizes 2048, 3072, 4096, 6144, 8192, and 16384. | | curves | An array of strings indicating the elliptic curve algorithms that are supported for enrollment through Keyfactor Command, if applicable. ECC curves may be specified using the well-known OIDs for ECC algorithms or by friendly name. Well-known OIDs include: 1.2.840.10045.3.1.7 = P-256/ prime256v1/ secp256r1 1.3.132.0.34 = P-384/secp384r1 1.3.132.0.35 = P-521/secp521r1
When specifying by friendly name, do not include a slash (use “P-256” or “secp256r1”, not “P-256/prime256v1/secp256r1”). |
|
| CertificateOwnerRole |
An integer indicating the certificate owner role setting. The supported values are:
-
0: Optional
-
1: Required
-
2: Hidden
Required is enforced for PFX and CSR enrollment in both the Management Portal and Keyfactor API. Hidden applies to PFX and CSR enrollment in the Management Portal.
|
| Key Info |
An object containing the supported key types along with the bit lengths and/or curves for the key types as appropriate.Show key info details.
Important: The KeyInfo parameter has been deprecated. It is retained for backwards compatibility, but all new development should use the PrimaryKeyAlgorithms and AlternativeKeyAlgorithms parameters.
| ECDSA |
An object containing the name of the key type and two arrays:
- name: A string indicating the name of the key type.
- bit_lengths: An array of integers indicating the key sizes supported for enrollment through Keyfactor Command.
- curves: An array of strings indicating the elliptic curve algorithms that are supported for enrollment through Keyfactor Command.
|
| RSA |
An object containing the name of the key type and two arrays:
- name: A string indicating the name of the key type.
- bit_lengths: An array of integers indicating the key sizes supported for enrollment through Keyfactor Command.
- curves: There are no curves for this type of key.
|
| Ed448 |
An object containing the name of the key type and two arrays:
- name: A string indicating the name of the key type.
- bit_lengths: An array of integers indicating the key sizes supported for enrollment through Keyfactor Command.
- curves: There are no curves for this type of key.
|
| Ed25519 |
An object containing the name of the key type and two arrays:
- name: A string indicating the name of the key type.
- bit_lengths: An array of integers indicating the key sizes supported for enrollment through Keyfactor Command.
- curves: There are no curves for this type of key.
|
| MLDSA44 |
An object containing the name of the key type and two arrays:
- name: A string indicating the name of the key type.
- bit_lengths: There are no key size choices for this type of key.
- curves: There are no curves for this type of key.
|
| MLDSA65 |
An object containing the name of the key type and two arrays:
- name: A string indicating the name of the key type.
- bit_lengths: There are no key size choices for this type of key.
- curves: There are no curves for this type of key.
|
| MLDSA87 |
An object containing the name of the key type and two arrays:
- name: A string indicating the name of the key type.
- bit_lengths: There are no key size choices for this type of key.
- curves: There are no curves for this type of key.
|
|
| PrimaryKeyAlgorithms |
An array of objects containing the supported primary key algorithms for the template including the bit lengths and/or curves as appropriate. Show primary key algorithm details.| name | A string indicating the name of the key algorithm. The supported key algorithm names are: ECDSA RSA Ed448 Ed25519 ML-DSA-44 ML-DSA-65 ML-DSA-87
| | bit_lengths | An array of integers indicating the key sizes supported for enrollment through Keyfactor Command. For RSA, Keyfactor Command supports key sizes 2048, 3072, 4096, 6144, 8192, and 16384. | | curves | An array of strings indicating the elliptic curve algorithms that are supported for enrollment through Keyfactor Command, if applicable. ECC curves may be specified using the well-known OIDs for ECC algorithms or by friendly name. Well-known OIDs include: 1.2.840.10045.3.1.7 = P-256/ prime256v1/ secp256r1 1.3.132.0.34 = P-384/secp384r1 1.3.132.0.35 = P-521/secp521r1
When specifying by friendly name, do not include a slash (use “P-256” or “secp256r1”, not “P-256/prime256v1/secp256r1”). |
|
| RFC Enforcement |
A Boolean that indicates whether RFC 2818 compliance enforcement is enabled (True or False). When this option is set to True, certificate enrollments made through Keyfactor Command for this template must include at least one DNS SAN. In the Keyfactor Command Management Portal, this causes the CN entered in PFX enrollment to automatically be replicated as a SAN, which the user can either change or accept. For CSR enrollment, if the CSR does not have a SAN that matches the CN, one will automatically be added to the certificate if this is set. By default, this is set to False at a system-wide level. |
|
| Extended Key Usages |
Currently not in use.
|
| Forest |
A string indicating the forest of the template. For Microsoft templates, this field is populated from Active Directory. For EJBCA templates, this field is populated from the Keyfactor Command CA record. The field is not configurable.
|
| Id |
An integer indicating the Keyfactor Command reference ID of the certificate template. |
| Key Size |
A string indicating the minimum supported key size of the template.
Note: This parameter is considered deprecated and may be removed in a future release.
|
| KeyRetention |
A string indicating the key retention type used to store private keys in Keyfactor Command for certificates enrolled with this template. Show key retention details.
| None |
The private key will not be retained. |
| Indefinite |
The private key will be retained until it is explicitly deleted. |
| After Expiration |
The private key will be retained until the specified number of days after the certificate expires (KeyRetentionDays), at which point it will be scheduled for deletion. |
| From Issuance |
The private key will be retained until the specified number of days after the date on which the certificate was issued (KeyRetentionDays), at which point it will be scheduled for deletion. |
|
| KeyRetentionDays |
An integer indicating the number of days a certificate’s private key will be retained in Keyfactor Command before being scheduled for deletion, if private key retention is turned on.
|
| KeyType |
A string indicating the key type of the template as returned by the CA.
Note: This parameter is considered deprecated and may be removed in a future release.
|
| Metadata Fields |
An array of objects containing template-level metadata field settings. Template-level metadata field configurations can override global metadata field configurations in these possible ways:
-
Configuration on the metadata field of required, optional, or hidden.
-
The default value for the metadata field.
-
A regular expression defined for the field (string fields only) against which entered data will be validated along with its associated message.
-
For fields of data type multiple choice, the list of values that appear in multiple choice dropdowns.
Metadata field settings defined on a template apply to enrollments made with that template only. When determining the default value for a metadata field, Keyfactor Command uses the first configured value found in this order:
-
The default value configured on the template’s default enrollment pattern.
-
The default value configured on the template.
-
The global default value configured for the metadata field.
Template-level metadata field settings, if defined, take precedence over global-level metadata field settings except when a default value is provided by the template’s default enrollment pattern.
Show metadata field details.
| Default Value |
A string containing the default value defined for the metadata field for the specific template. |
| Enrollment |
An integer that indicates how metadata fields should be handled on the PFX and CSR Enrollment pages. Possible values are:
|
0
|
Optional Users have the option to either enter a value or not enter a value in the field. |
|
1
|
Required Users are required to enter data in the field when populating metadata fields on the PFX and CSR Enrollment pages. The field is not required on the certificate details or Add Certificate page. |
| 2 |
Hidden The field is hidden and does not appear on the PFX and CSR Enrollment pages. This field still appears on the certificate details and the Add Certificate page. |
|
| Id |
An integer indicating the Keyfactor Command reference ID of the template-specific metadata setting. |
| Message |
A string containing a message to present when a user enters information in a metadata field that does not match the template-specific regular expression (Validation field). |
| Metadata Id |
An integer indicating the global metadata field associated with the template-specific settings. |
| Validation |
A string containing the template-specific regular expression against which data entered in a string field will be validated. When a user enters information in a metadata field that does not match the specified regular expression, he or she will see the warning message specified in the Message field. For example:Copy^[a-zA-Z0-9'_\.\-]*@(keyexample\.org|keyexample\.com)$
This regular expression specifies that the data entered in the field must consist of some number of characters prior to the @ made up only of lowercase letters, uppercase letters, numbers, apostrophes, underscores, periods, and/or hyphens followed by exactly either @keyexample.org or keyexample.com. This field is only supported for metadata fields with data type string. |
For example:
Copy
"MetadataFields": [
   {
      "Id": 4,
      "DefaultValue": "reggie.wallace@keyexample.com",
      "MetadataId": 4,
      "Validation": "^[a-zA-Z0-9'_\\.\\-]*@(keyexample\\.org|keyexample\\.com)$",
      "Enrollment": 1,
      "Message": "Your email address must be of the form user@keyexample.com or fname.lname@keyexample.com."
   },
   {
      "Id": 13,
      "DefaultValue": "E-Business",
      "MetadataId": 5,
      "Validation": "",
      "Enrollment": 0,
      "Message": "",
      "Options": "Accounting,E-Business,Executive,HR,IT,Marketing,R&D,Sales"
   }
]
|
| Name |
A string containing the common name (short name) of the template. This name typically does not contain spaces. For a template created using a Microsoft management tool, this will be the Microsoft template name. |
| Regexes |
An array of objects containing the global template regular expression settings. These apply to all enrollments that are not otherwise overridden by individual template settings, including those that do not use a template (for example, from a standalone CA). Show regular expression details.
| Template Id |
An integer indicating the Keyfactor Command reference ID of the certificate template the regular expression is associated with. |
| Subject Part |
A string indicating the portion of the subject the regular expression applies to (for example, CN). |
| RegEx |
A string specifying the regular expression against which data entered in the indicated subject part field (for example, CN) in the enrollment pages of the Keyfactor Command Management Portal or using an API enrollment operation will be validated.
Use the GET Templates Subject Parts operation to retrieve a list of all the supported subject parts.
| CN (Common Name) |
This regular expression specifies that the data entered in the field must consist of 1 to 63 characters in the first portion of the field made up only of lowercase letters, uppercase letters, numbers, periods, and/or hyphens (but not at the beginning or end of sections or duplicated) followed by exactly .keyexample.com:
Copy
^(?!-)(?!.*--)[A-Za-z0-9-]{1,63}(?<!-)(\.[A-Za-z0-9-]{1,63})*\.keyexample\.com$
The default value for the Common Name regular expression is:
This requires entry of at least one character in the Common Name field in the enrollment pages.
|
| O (Organization) |
This regular expression requires that the organization name entered in the field be one of “Key Example Inc”, “Key Example” or “Key Example Inc.”:
Copy
^(?:Key Example Inc|Key Example|Key Example, Inc\.)$
The period in the final company name (Key Example, Inc.) needs to be escaped in the regular expression with a slash ("\") but the comma does not.
|
| OU (Organization Unit) |
This regular expression requires that the organizational unit entered in the field be one of these four departments:
Copy
^(?:IT|HR|Accounting|E-Commerce)$
|
| L (City/ Locality) |
This regular expression requires that the city entered in the field be one of these five cities:
Copy
^(?:Boston|Chicago|New York|London|Dallas)$
|
| ST (State/ Province) |
This regular expression requires that the state entered in the field be one of these eight states:
Copy
^(?:Massachusetts|Illinois|New York|Ontario|Texas)$
|
| C (Country) |
This regular expression requires that the country entered in the field be either US or CA:
|
| E (Email) |
This regular expression specifies that the data entered in the field must consist of some number of characters prior to the “@” made up only of lowercase letters, uppercase letters, numbers, periods, underscores, percent signs, apostrophes, plus signs, and/or hyphens followed by exactly “@keyexample.com”:
Copy
^[A-Za-z0-9._%'+-]+@keyexample\.com$
|
| DNS (Subject Alternative Name: DNS Name) |
This regular expression specifies that the data entered in the field must consist of 1 to 63 characters in the first portion of the field made up only of lowercase letters, uppercase letters, numbers, periods, and/or hyphens (but not at the beginning or end of sections or duplicated) followed by exactly either “.keyexample1.com” or “.keyexample2.com”:
Copy
^(?!-)(?!.*--)[A-Za-z0-9-]{1,63}(?<!-)(\.[A-Za-z0-9-]{1,63})*\.(keyexample\.com|keyexample2\.com)$
|
| IPv4 (Subject Alternative Name: IPv4 Address) |
This regular expression specifies that the data entered in the field must be exactly “130.101.” followed by a value between 0 and 255, followed by “.”, followed a value between 0 and 255:
Copy
^130\.101\.(?:[0-9]|[1-9][0-9]|1[0-9]{2}|2[0-4][0-9]|25[0-5])\.(?:[0-9]|[1-9][0-9]|1[0-9]{2}|2[0-4][0-9]|25[0-5])$
This regular expression specifies only that the IPv4 address is made up of 4 sets of values between 0 and 255 separated by periods:
Copy
^(?:[0-9]{1,2}|1[0-9]{2}|2[0-4][0-9]|25[0-5])\.(?:[0-9]{1,2}|1[0-9]{2}|2[0-4][0-9]|25[0-5])\.(?:[0-9]{1,2}|1[0-9]{2}|2[0-4][0-9]|25[0-5])\.(?:[0-9]{1,2}|1[0-9]{2}|2[0-4][0-9]|25[0-5])$
|
| IPv6 (Subject Alternative Name: IPv6 Address) |
This regular expression specifies that the data entered in the field must be made up of up to eight sets of between one and four numbers and/or uppercase letters separated by colons:
Copy
^([A-F0-9]{1,4}:){1,7}([A-F0-9]{1,4})?(\:\:([A-F0-9]{1,4}:){0,6}[A-F0-9]{1,4})?$
This regular expression optionally matches a shorthand “::” that can replace one or more groups of zero segments, allowing the address to use shorthand notation.
|
| MAIL (Subject Alternative Name: Email) |
This regular expression specifies that the data entered in the field must consist of some number of characters prior to the “@” made up only of lowercase letters, uppercase letters, numbers, periods, underscores, percent signs, apostrophes, plus signs, and/or hyphens followed by exactly “@keyexample.com”:
Copy
^[A-Za-z0-9._%'+-]+@keyexample\.com$
|
| UPN (Subject Alternative Name: User Principal Name) |
This regular expression specifies that the data entered in the field must consist of between 1 and 64 characters prior to the “@” made up only of lowercase letters, uppercase letters, numbers, apostrophes, underscores, spaces, and/or hyphens followed by exactly “@keyexample.com”:
Copy
^[A-Za-z0-9'_ -]{1,64}@keyexample\.com$
|
|
| Error |
A string specifying the error message displayed to the user when the subject part referenced in the CSR or entered for a PFX enrollment does not match the given regular expression.
Note: The error message already includes a leading string with the subject part (for example, Common Name: or Invalid CN provided: depending on the interface used). Your custom message follows this.
|
|
| Requires Approval |
A Boolean indicating whether the template has been configured with the Microsoft CA certificate manager approval option enabled (True or False). |
| RFC Enforcement |
A Boolean indicating whether certificate enrollments made through Keyfactor Command for this template must include at least one DNS SAN (True or False). In the Keyfactor Command Management Portal, this causes the CN entered in PFX enrollment to automatically be replicated as a SAN, which the user can either change or accept. For CSR enrollment, if the CSR does not have a SAN that matches the CN, one will automatically be added to the certificate if this is set. By default, this is set to False at a system-wide level and may be overridden on a template-by-template basis. |
|
 ) in the Management Portal.